Independent EU Built by ServiceNow's former Principal Security Advisor, EMEA
The security specialist for the ServiceNow AI Platform.
Your custom code, ACLs, integrations, Vault and AI agents are the layer ServiceNow does not secure for you. Nowisor reads it with an open-source engine, judges it with ten years from inside ServiceNow's Office of the CISO, and signs the finding when your auditor asks.

Fix first — what to change this week, ranked by risk released per unit of effort. Captured from a ServiceNow developer instance.
Ten years inside ServiceNow
Principal Security Advisor, Office of the CISO, EMEA
Black Hat Arsenal
Co-founder and Review Board member
Open-source engine
Apache-2.0. Inspect it, fork it, run it yourself
European by design
Stored in Amsterdam, AI in Frankfurt, fail-closed
Expertise
What a specialist sees in the first scan
Patterns we meet in most instances. Security Center tells you a setting is off. We show you the path, on your release, in your code.
The go-live ACL
An out-of-the-box ACL loosened to true during a go-live two releases ago, never reverted.
The client-callable query
A Script Include reachable through GlideAjax that queries with no condition — client-callable and unlogged.
The integration nobody owns
An integration user holding admin, last token use fourteen months ago, credential never rotated.
The agent with the wrong mask
An AI agent running as a user whose role mask reaches HR case data it was never meant to touch.
Inside the product
From posture to the exact record, in one scan
What the engine shows after a scan. Each screen below was captured from a ServiceNow developer instance; nothing in it is a customer's.


Active Risk
A misconfiguration is a finding. One that somebody used last week is a priority.
Active Risk binds each scan finding to seven days of your own runtime logs, so you stop arguing about severity and start with the findings that were actually exercised.
- sys_audit sysevent syslog_transaction
- Read-only scripts, safe for production
- No connection or OAuth required
- Exercised
- The logs show this weakness was used in the last seven days. Fix it first, and look at who used it.
- Dormant
- The misconfiguration is there, and nothing touched it in the window. Schedule it; do not page anyone.
- Investigate
- Activity near the finding that the logs alone cannot explain. A named expert reads it with you.
- Noise
- Matches the pattern, explained by expected behaviour. Recorded with its reason, then set aside.

What we cover
Five surfaces. Four read by the engine, one reviewed by the expert.
The controls are already there. Most instances have never turned them on. If we can't read it conclusively, the verdict says so — silence is never rendered as good news.
01Engine
AI agents, Otto and AI Specialists
Which agents, Otto skills and AI Specialists run in your tenant, what each one runs as, and what its role mask lets it reach. Exercised versus dormant, from seven days of logs.
02Engine
The code your team wrote
Script includes, business rules, UI actions and ACL scripts read as syntax, not as settings. The surface a checklist cannot reach by construction.
03Engine
Configuration and identity
Hardening properties against your release baseline, session and authentication controls, and the role model as it stands today rather than as it was designed.
04Engine
Non-human identities
Integrations, OAuth clients and their last token use, stored credentials, MID Servers and scheduled jobs.
05Expert
ServiceNow Vault
Encryption contexts, anonymisation on clones, secrets management and code signing — reviewed by the expert, not scanned by the engine.
Who reviews your instance
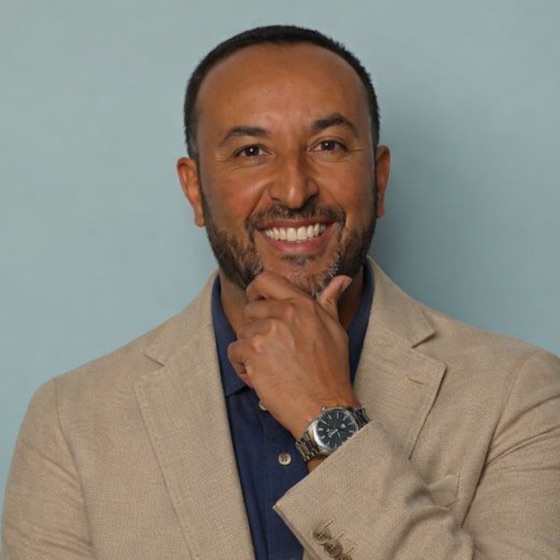
Rachid Harrando
Founder, Nowisor SASU, Nice
- Ten years as Principal Security Advisor, ServiceNow Office of the CISO, EMEA
- Co-founder of Black Hat Arsenal and Review Board member
- 25 years in cybersecurity, from embedded systems to platform security
Author of Securing ServiceNow: A CISO's Field Guide. The person who reviews your instance is the person who presents the findings.
How it works
Engine, expert, evidence
01
Engine
Open source under Apache-2.0. Runs as a suite scan inside ServiceNow's own Instance Scan framework, or from a results file your team uploads. Starts from your Security Center score and adds what a settings comparison cannot reach.
02
Expert
Every report is reviewed and signed by a named security expert. The person who signs the finding is the person who takes your auditor's call.
03
Evidence
When a regulator asks, the finding is already mapped — DORA, NIS2, ISO 27001, NCA ECC — and signed. Produced on request, not pushed.
Work with us
Scoped and signed by a named expert
Start with a fixed-price Baseline. For annual engagements, a scope and a fixed price within five working days of a 30-minute call.
Baseline Assessment
€9,900 fixed price
A first engagement on one production instance. Nine expert days over 30 calendar days, with 30 days of Connected included. Additional instances are priced per scope. Credited in full against an annual engagement signed within 90 days.
Access Read-only API, or results-file upload for self-hosted
Assured
A single regulated organisation, up to three instances. Continuous posture, quarterly signed evidence packs, 48-hour advisory verdicts, eight hours a quarter of auditor support, and direct access to the named SME.
Access Connected
Programme
Multi-entity groups, MSPs and partners, or platforms mid-migration. Everything in Assured plus architecture review, programme design, delivery capacity and quarterly CISO governance. Local install available on request.
Access Any
Self-Hosted Assurance
Self-hosted or egress-locked instances that cannot be reached from outside. Advisory verdicts within 48 hours on your release, one upgrade security delta a year, two platform reviews, two signed evidence packs, and four hours a quarter with your auditor. Runs from a scoped application you install through your own change process, or our five standalone Background Scripts for a reduced review.
Access Upload only — nothing connects inward, no credentials leave your side
Vault Implementation Review
You own ServiceNow Vault. What is deployed, what is scoped wrong, and what the integrations still bypass. Five expert days and a written plan. Credited against Assured.
Access Read-only API, or results-file upload for self-hosted
Prefer to look first? Run the open-source engine yourself, free — read-only, inside your own tenant, nothing connected.
European by design, open by default
Accounts, scan snapshots and configuration values are stored and scanned in Amsterdam. On Connected and above, AI analysis can run entirely on EU infrastructure in Frankfurt under a signed GDPR Article 28 agreement, and when the EU route is selected the system fails closed: if it is unavailable, the request is refused, never rerouted.
- Your instance
- Amsterdam
- Frankfurt
The detection engine is open source under Apache-2.0. The advisory is the value; the detection is the floor, and the floor is yours.
FAQ
Common questions
How is this different from ServiceNow Security Center?
It runs alongside it, and it starts from it. Security Center scores your configuration against ServiceNow's own hardening checklist. Nowisor reads that score as the platform baseline rather than recomputing it, then adds what a settings comparison cannot reach: static analysis of your custom Script Includes, Business Rules and UI Actions, out-of-the-box ACLs that were modified, and the attack paths that chain findings together. Run both — complementary, never a replacement.
How is this different from AI Control Tower?
AI Control Tower is ServiceNow's governance console for the agents, skills and models it knows about. Nowisor reads the other side: what each agent runs as, which role mask it carries, which tables that mask reaches, and whether it was exercised in the last seven days of logs. Control Tower governs the agent; Nowisor shows what the agent can touch.
Can I see a report before I connect anything?
Yes — a redacted sample of each report is available on request.
Is this a managed SOC?
No. There is no 24/7 monitoring and no incident retainer. Findings arrive on a scheduled cadence and advisories are scored on disclosure; under Assured you get a verdict on your instance within 48 hours. Detection and response stay in your SIEM and your SOC.
What instance access does Nowisor require?
None to start: you run the open-source detection scripts in your own tenant and paste the output. A connected engagement adds a read-only OAuth integration scoped to specific tables. Self-hosted instances upload a results file and nothing connects inward. The only write, ever, is a remediation ticket you confirm per action.
Which ServiceNow versions are supported?
Washington DC through current GA. Every check is verified against your instance, on your release, at scan time. Where a check cannot be verified with the read-only connection, it reports UNKNOWN with the reason — never a pass or a skip. Each path reads things the other does not. An upload, which runs in your instance, reads the plugin inventory and the tables ServiceNow keeps off its web-service API. An upload does not yet carry the record creator, the OAuth client and scope reads or exposure context, which the connection reads. Checks for features your instance doesn't have report as not applicable when verified from an upload, or UNKNOWN over the read-only connection — never as a pass.
Does my ServiceNow data get sent to the AI model?
Yes — to answer you, your query plus relevant context is sent to our AI provider over an encrypted API. We never send passwords, API keys or OAuth tokens. By default, anything carrying instance data is routed to the EU inference path, enforced in code, and a request the selected option cannot serve is refused, never re-routed. If your policy prohibits this, the open-source scripts run entirely on your side with nothing leaving your instance.