Independent EU Built by ServiceNow's former Principal Security Advisor, EMEA
The security specialist for the ServiceNow AI Platform.
Your custom code, ACLs, integrations, Vault and AI agents are the layer ServiceNow does not secure for you. Nowisor reads it with an open-source engine, judges it with ten years from inside ServiceNow's Office of the CISO, and signs the finding when your auditor asks.
What a specialist sees in the first scan
Patterns we meet in most instances. Security Center tells you a setting is off. We show you the path, on your release, in your code.
The go-live ACL
An out-of-the-box ACL loosened to true during a go-live two releases ago, never reverted.
The client-callable query
A Script Include reachable through GlideAjax that queries with no condition — client-callable and unlogged.
The integration nobody owns
An integration user holding admin, last token use fourteen months ago, credential never rotated.
The agent with the wrong mask
An AI agent running as a user whose role mask reaches HR case data it was never meant to touch.
What we cover
The controls are already there. Most instances have never turned them on. We cover the five surfaces where that happens — four read by the engine, one reviewed by the expert. If we can't read it conclusively, the verdict says so — silence is never rendered as good news.
AI agents, Otto and AI Specialists
Which agents, Otto skills and AI Specialists run in your tenant, what each one runs as, and what its role mask lets it reach. Exercised versus dormant, from seven days of logs.
The code your team wrote
Script includes, business rules, UI actions and ACL scripts read as syntax, not as settings. The surface a checklist cannot reach by construction.
Configuration and identity
Hardening properties against your release baseline, session and authentication controls, and the role model as it stands today rather than as it was designed.
Non-human identities
Integrations, OAuth clients and their last token use, stored credentials, MID Servers and scheduled jobs. The identities that never log in and never leave.
ServiceNow Vault
Encryption contexts, anonymisation on clones, secrets management and code signing — reviewed by the expert, not scanned by the engine. See Vault Implementation Review.
Who reviews your instance
Built by a ServiceNow security defender, for ServiceNow security defenders
Rachid Harrando
Founder, Nowisor SASU, Nice
- Ten years as Principal Security Advisor, ServiceNow Office of the CISO, EMEA
- Co-founder of Black Hat Arsenal and Review Board member
- 25 years in cybersecurity, from embedded systems to platform security
Author of Securing ServiceNow: A CISO's Field Guide. The person who reviews your instance is the person who presents the findings.
How it works
Engine
Open source under Apache-2.0, runs as a suite scan inside ServiceNow's own Instance Scan framework, or from a results file your team uploads. Starts from your Security Center score and adds what a settings comparison cannot reach: your code, your modified ACLs, your agents.
Expert
Every report is reviewed and signed by a named security expert. The person who signs the finding is the person who takes your auditor's call.
Evidence
When a regulator asks, the finding is already mapped — DORA, NIS2, ISO 27001, NCA ECC — and signed. Produced on request, not pushed.
Inside the product
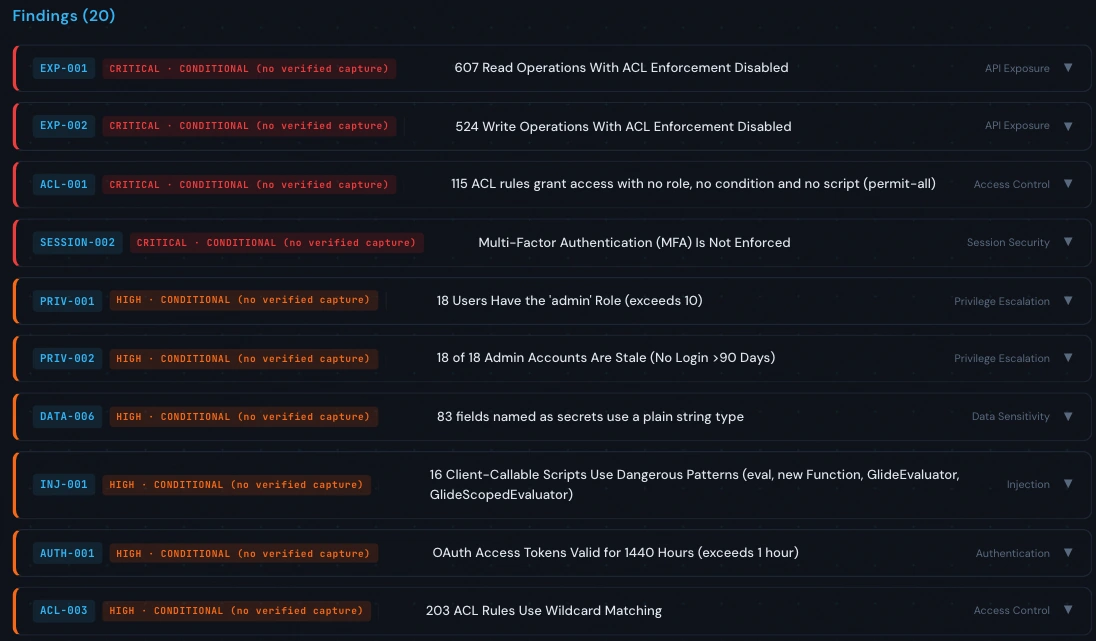
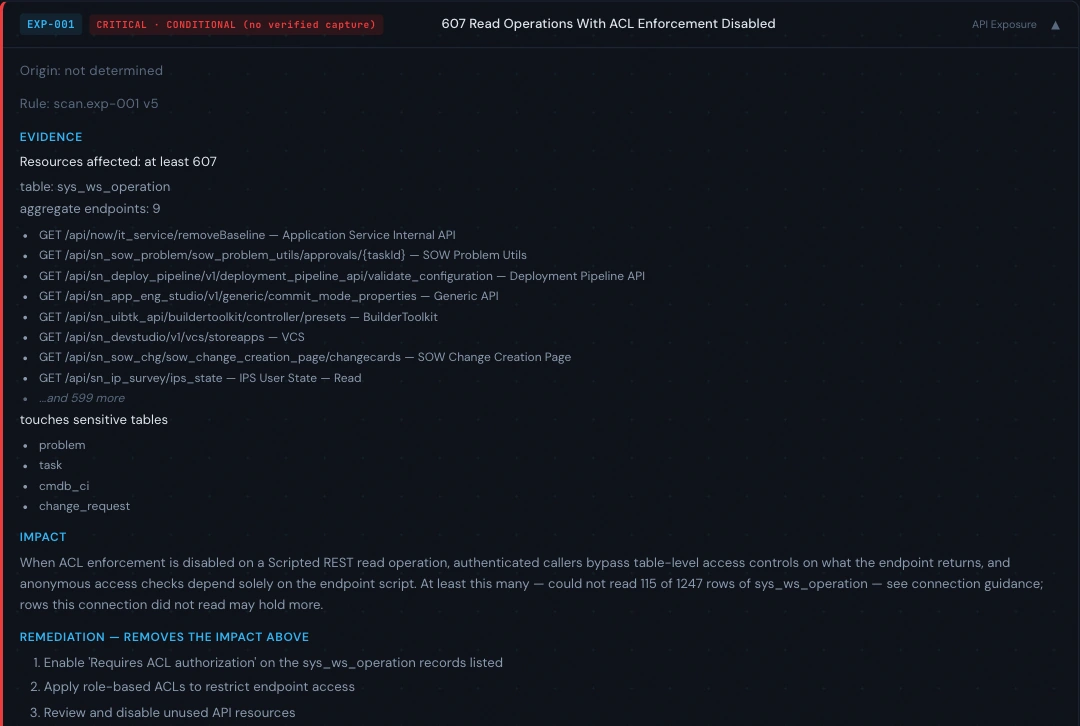
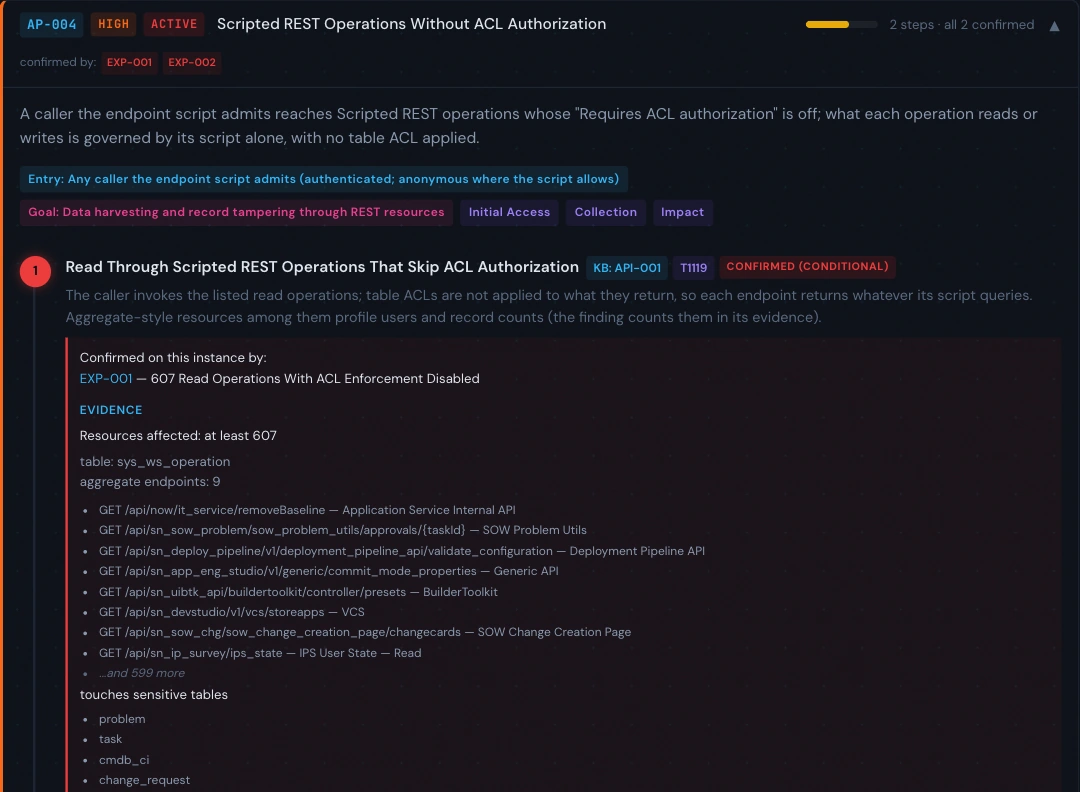
What the engine shows after a scan. Each screen below was captured from a ServiceNow developer instance; nothing in it is a customer's.
Work with us
Scoped and signed offline. A named security expert carries the finding, takes your auditor's call and signs the evidence. A scope and a fixed annual price within five working days of a 30-minute call.
Book a 30-minute scoping call| Engagement | For | Access |
|---|---|---|
| Baseline Assessment | A first engagement on one production instance. Nine expert days over 30 calendar days, with 30 days of Connected included. Additional instances are priced per scope. Credited in full against an annual engagement signed within 90 days. | Read-only API, or results-file upload for self-hosted |
| Assured | A single regulated organisation, up to three instances. Continuous posture, quarterly signed evidence packs, 48-hour advisory verdicts, eight hours a quarter of auditor support, and direct access to the named SME. | Connected |
| Programme | Multi-entity groups, MSPs and partners, or platforms mid-migration. Everything in Assured plus architecture review, programme design, delivery capacity and quarterly CISO governance. Local install available on request. | Any |
| Self-Hosted Assurance | Self-hosted or egress-locked instances that cannot be reached from outside. Advisory verdicts within 48 hours on your release, one upgrade security delta a year, two platform reviews, two signed evidence packs, and four hours a quarter with your auditor. Runs from a scoped application you install through your own change process, or our five standalone Background Scripts for a reduced review. | Upload only — nothing connects inward, no credentials leave your side |
| Vault Implementation Review | You own ServiceNow Vault. What is deployed, what is scoped wrong, and what the integrations still bypass. Five expert days and a written plan. Credited against Assured. | Read-only API, or results-file upload for self-hosted |
Or run the engine yourself
Three plans run inside your own tenant with nothing connected. Connected is priced per production instance it watches.
| Plan | For | Price | Includes | Next step |
|---|---|---|---|---|
| Recon | Find out in an afternoon whether your instance has a problem worth escalating. | €0 |
| Start free |
| Practitioner | For the person who owns the tenant and gets the call when something is wrong with it. | €149/mo |
| Start 14-day trial |
| Practice | For a practice whose reputation rides on the same answer being right at every client. | €499/mo |
| Start 14-day trial |
| Connected | For a production instance where "we think it is fine" is not an answer you can give. | €2,900/mo, billed annually (€34,800) |
| Request invoice |
All plans include the open-source detection engine. Monthly plans switch or cancel anytime. Data is hosted in the EU, EU-only AI processing is available on Connected and above, and a DPA is available.
What you receive
Each report is signed by the person who reviewed it. A redacted sample of each is available on request.
Instance Security Report
Posture by category, every finding with the property or record it was read from and the release it was evaluated against.
Sample available on requestActive Risk Report
Each finding correlated against seven days of runtime activity and marked exercised, dormant, noise or investigate.
Sample available on requestQuarterly Security Review
Verdicts, findings register with SLAs, and a sign-off by a named security expert. The artifact your auditor asks for.
Sample available on requestLatest advisories
Pulled from the advisory tracker. The tracker reads the ServiceNow CNA, NVD, CISA KEV, GitHub and VulnCheck daily.
European by design, open by default
Accounts, scan snapshots and configuration values are stored and scanned in Amsterdam. On Connected and above, AI analysis can run entirely on EU infrastructure in Frankfurt under a signed GDPR Article 28 agreement, and when the EU route is selected the system fails closed: if it is unavailable, the request is refused, never rerouted.
The detection engine is open source under Apache-2.0. Inspect it, fork it, or run the detection yourself without depending on nowisor.com at all. The advisory is the value; the detection is the floor, and the floor is yours.
Common questions
How is this different from ServiceNow Security Center?
It runs alongside it, and it starts from it. Security Center scores your configuration against ServiceNow's own hardening checklist — ACL coverage, properties, OAuth, MID Server, audit and session settings — and that overlap is real. When you connect an instance, Nowisor reads that score and treats it as the authoritative platform baseline rather than recomputing it, then adds what a settings-comparison framework cannot reach by construction: static analysis of your custom Script Includes, Business Rules, and UI Actions, and detection of out-of-the-box ACLs that were modified. It also chains findings into the cross-domain attack paths an adversary would actually walk, and maps each one to the NIS2, DORA, ISO 27001 or NCA ECC control an auditor will ask about. Security Center tells you a setting is off; Nowisor shows you the reachable path. Run both — complementary, never a replacement.
How is this different from AI Control Tower?
AI Control Tower is ServiceNow's governance console for the agents, skills and models it knows about: inventory, usage, guardrails. Nowisor reads the other side — what each agent runs as, which role mask it carries, which tables that mask reaches, and whether it was exercised in the last seven days of logs. Control Tower governs the agent; Nowisor shows what the agent can touch. Run both.
Can I see a report before I connect anything?
Yes — a redacted sample of each report is available on request.
Is this a managed SOC?
No. There is no 24/7 monitoring and no incident retainer. Findings arrive on a scheduled cadence, and advisories are scored on disclosure; under Assured you get a verdict on your instance within 48 hours. Detection and response stay in your SIEM and your SOC.
What instance access does Nowisor require?
Recon (free) requires no instance access — you copy & run the open-source detection scripts, and every plan below Connected stays that way: the scan pack runs in your tenant and you paste its output. Connected adds a read-only OAuth integration scoped to specific tables. Read-only by default; on Managed, the only write is an explicit remediation ticket you confirm per action.
Which ServiceNow versions are supported?
Washington DC through current GA. Every check is verified against your instance, on your release, at scan time. Where a check cannot be verified with the read-only connection, it reports UNKNOWN with the reason — never a pass or a skip — and is fully verified from an upload. Checks for features your instance doesn't have report as not applicable when verified from an upload, or UNKNOWN over the read-only connection — never as a pass.
Does my ServiceNow data get sent to the AI model?
Yes — to answer you, your query plus relevant context (knowledge-base articles and, if you've connected an instance, your scan findings and configuration values such as hardening property settings) is sent to our AI provider (Anthropic's Claude or OpenAI) over an encrypted API. We never send passwords, API keys, or OAuth tokens. By default, anything carrying instance data is routed to our EU inference path rather than to the shared US endpoint, and that routing is enforced in code. Connected accounts and above can enable Enhanced data protection (requests go to a separate, dedicated Anthropic workspace key rather than the shared one, processed in the US), or EU data residency, which routes inference through an EU-hosted gateway to Claude models pinned to EU regions (Frankfurt) under a GDPR Art. 28 DPA. On that EU option we have switched prompt and output logging off at the gateway, so under that same DPA it keeps no copy of either. The model behind it is served by AWS Bedrock in eu-central-1 (Frankfurt) under its own terms, which makes this EU-resident processing with no gateway-side logging rather than end-to-end zero retention. Retention and model-training terms for those two options come from our agreements with those providers rather than a setting in the product; what the product enforces is that a request the selected option cannot serve is refused and the credit refunded, never re-routed to the standard endpoint. If your policy prohibits sending configuration data to a third-party model, the open-source detection scripts (Recon) run entirely on your side with nothing leaving your instance.
Know where your ServiceNow AI Platform is exposed. Show your work when asked.
Start with the free tier and the open-source checks, or book thirty minutes and get a scope and a fixed price within five working days.